


 leaked API keys

Fragmented data
Sources sit in separate tools, with no shared picture of the threat.
OwlClaw brings dark-web search, breach exposure checks, OSINT investigations, Telegram monitoring and AI-assisted briefs into one workspace, so your team finds what's leaked, who's behind it and what to do next.
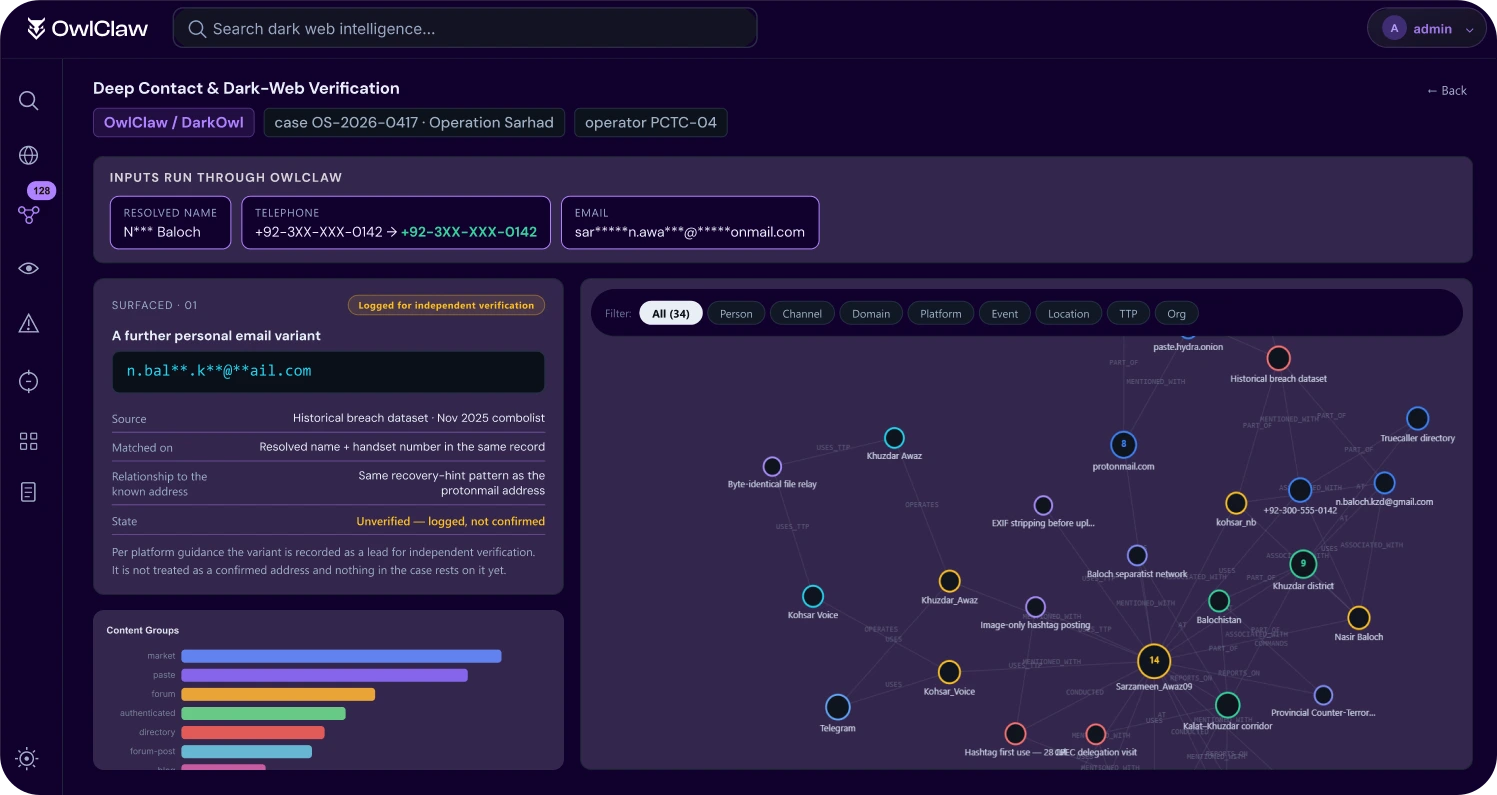
One platform for four intelligence sources. OwlClaw collects from dark-web forums and markets, breach repositories, social media and Telegram, then turns scattered data into structured, actionable intelligence.
 Total Queries
 Documents
 Emails Found
 Credential Hits
 CVEs Mentioned
 CCNs Found
From the first search to an approved brief, without switching tools.
crawled records
Emails and leaked records, indexed and searchable in one place.
Telegram chats
Channels and groups monitored for new posts, actors and keywords.
Onion pages collected every hour
Fresh dark-web content, gathered around the clock.
Risk from dark-web activity, leaked credentials, underground forums and Telegram channels grows faster than teams can review it by hand.
 6 Gaps
One threat, spread across too many tools.
Most teams piece together dark-web, breach, social and Telegram data by hand and signal gets lost on the way
OwlClaw closes each gap in one workspace

Sources sit in separate tools, with no shared picture of the threat.
Analysts lose hours pivoting between search, evidence and reporting.
Genuine threats are hard to separate from noise at volume.
Little visibility into exposed credentials and leaked records.
Links between people, domains and organizations go unmapped.
No consistent brief format or approval workflow for output.
Search, assess, monitor, report. OwlClaw's six modules take your team from the first dark-web search to an AI-assisted assessment, continuous monitoring and an approved intelligence brief, all in one workspace.


Search organizations, domains, emails, IPs, credentials and threat terms across indexed sources.
Results are grouped by source type (market, forum, paste site, blog, news), with counts of emails, credentials, IPs, card numbers, crypto wallets and CVEs found.
Review forums, markets, ransomware sites and paste sources, with their threat-score history.
Judge how credible a source is before you act on what it says.
Get an initial verdict, confidence level, key findings and suggested next steps.
Analysts start from a draft assessment instead of a blank page.
Monitor Telegram channels, keywords, actors and digital assets, with a notification for every new hit.
Alerts are tagged by severity and source, so the urgent ones surface first.
Analyze public profiles with timeline, evidence, media, geography, forecast and compliance sections.
One structured report replaces scattered notes and screenshots.
Edit, approve, discard or export reports through analyst and commander workflows.
AI drafts the brief; your people review and approve it before it leaves the platform.
OwlClaw collects intelligence from dark-web sources, breach repositories, social media and Telegram, then converts fragmented data into structured, actionable intelligence.
Collection runs on schedule across every source, so nothing depends on someone remembering to search.
Dark-web and underground-source discovery · Data-breach and credential exposure monitoring · Telegram and social-media intelligence · Automated collection scheduling
See who is behind the activity and how people, domains and organizations connect.
Threat-actor identification and tracking · Entity extraction and link analysis · Geographic and behavioural analysis
Every finding comes with a score and a confidence level, so teams act on evidence, not noise.
Organization and individual risk assessment · Threat scoring and confidence assessment · Escalation and predictive risk analysis
Watch what matters and see how it has changed over time.
Keyword and entity-based continuous monitoring · Real-time alert generation · Timeline and historical activity analysis
Every case is kept on record, leadership sees the summary, and each role sees only what it should.
Investigation history and case management · Executive intelligence dashboards · Role-based access for admins, analysts and commanders
Four steps, one workspace. Every finding moves from raw signal to a decision your leadership can act on.
Step 01
Query any organization, domain, email, IP, credential or keyword across dark-web, breach, OSINT and Telegram sources at once.
 leaked API keys
Step 02
AI returns an initial verdict with a confidence level, key findings and next steps, beside each source's threat-score history.
 AI verdict
 confidence
Step 03
Add the entity to a watchlist. OwlClaw keeps collecting on schedule and alerts you to every new hit.
 Telegram - New Post
 watchlists - 3 keywords
Step 04
Analysts edit the AI-drafted brief, commanders approve it, and the final report is exported or shared.
 Intelligence Brief
 Analyst - Commander
OwlClaw is a dark-web and open-source intelligence platform. It brings dark-web search, breach exposure checks, OSINT investigations, Telegram monitoring and AI-assisted briefs into one workspace.
Dark-web forums and markets, ransomware leak sites, paste sites, breach repositories, social media and Telegram channels.
It gives a first verdict, a confidence level, key findings and suggested next steps. Analysts review and edit it, and commanders approve the final brief before export.
Yes. Watchlists cover Telegram channels, keywords, threat actors and digital assets such as domains, and alert you to every new hit.
OwlClaw has three roles: admins manage the platform, analysts investigate and draft, and commanders review and approve.
Deployment and data-hosting options are covered in a guided demo. Request a demo and our team will walk you through them.
See how OwlClaw surfaces leaked credentials, underground chatter and threat-actor activity linked to your organization, in a guided walkthrough.